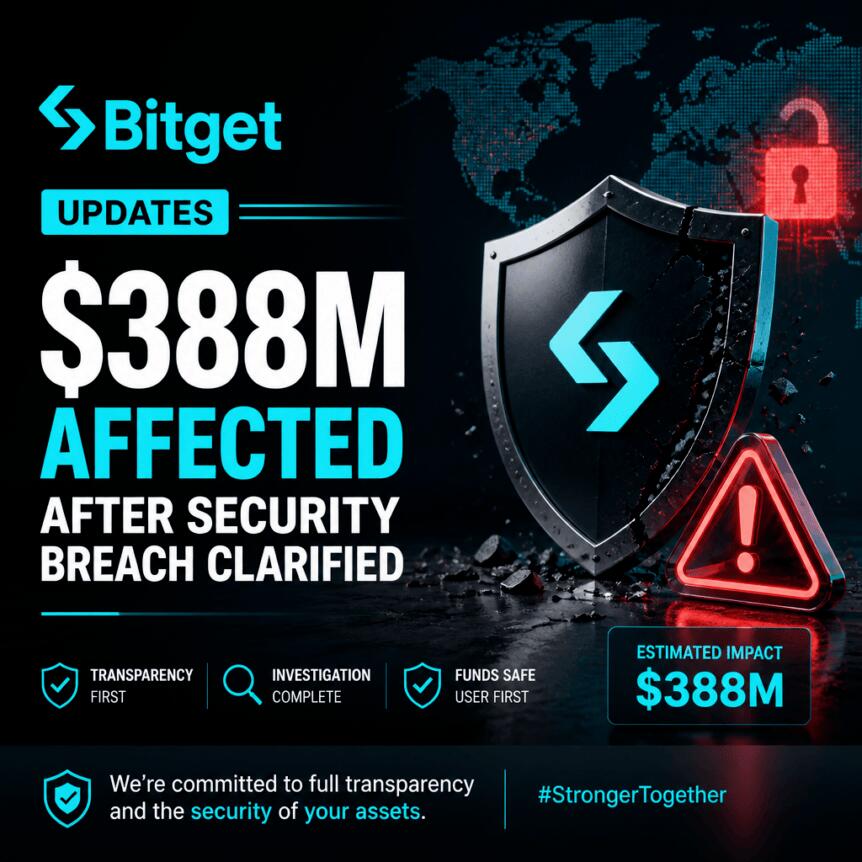
Bitget has revised the scale of its security breach after initially reporting a smaller figure for the amount of crypto impacted. In an updated incident report, the exchange said roughly $388 million in assets were affected—higher than Thursday’s estimate of $352 million.
In a follow-up update on Friday, Bitget also confirmed it would continue pausing withdrawals while it investigates, and it introduced a bounty program designed to encourage the freezing or recovery of stolen funds. The exchange attributed the upward revision to a more complete accounting of transfers during the incident, including assets on networks not captured in the first report.
Key takeaways
- Bitget revised the breach impact to about $388 million, up from the previously reported $352 million.
- About $387.5 million was traced to attacker-controlled addresses, based on onchain monitoring—around $35 million more than previously disclosed.
- Withdrawals remain paused, while the exchange says the incident is contained and no further unauthorized transfers are possible.
- Bitget says the change reflects fuller accounting, including additional affected assets on Zcash and TRON that were missing from the initial estimate.
- The breach involved multiple networks, including EVM chains, the XRP Ledger, Zcash, and TRON, with multiple asset types listed.
Recalculated losses: what changed in Bitget’s numbers
Bitget’s revised incident report clarifies that the affected amount was understated in the first estimate. According to the exchange, its revised figures reflect a more complete accounting of transfers that occurred during the breach—specifically by adding affected assets on Zcash and TRON that were not included in the initial calculation.
Bitget emphasized that the update does not indicate additional theft beyond what was already captured during the incident window. The company stated that the incident remains contained and that no further unauthorized transfers are possible.
In practical terms for users and market participants, the revision matters because it changes how investors assess the severity of the event and the scope of remediation Bitget must carry out—particularly for assets moved to addresses controlled by the attackers.
Where the funds went: tracing to attacker-controlled addresses
Alongside the updated total, Bitget reported that $387.5 million were transferred to attacker-controlled addresses according to onchain tracing. That figure is about $35 million higher than what was reported on Thursday.
The exchange framed the difference as an accounting refinement rather than an expansion of the breach’s duration or a new wave of withdrawals being stolen. Bitget said the updated estimate includes additional transfers involving assets on Zcash and TRON, helping align its reported figures with a more comprehensive view of movement across affected chains.
For traders and users, the most important operational takeaway is that Bitget’s control measures continue—withdrawals are still paused—while the company focuses on identifying and potentially freezing or recovering funds connected to the hack.
Networks and assets named in the incident update
Bitget said the incident involved addresses spanning multiple ecosystems, including Ethereum Virtual Machine (EVM) networks, the XRP Ledger, Zcash, and TRON. The exchange listed a range of assets that were stolen, including:
The follow-up report, however, did not directly address comments made by Bitget CEO Gracy Chen on Thursday. Earlier coverage from Cointelegraph noted her speculation that a North Korean hacking group may have been behind the attack, citing what she described as IP-related clues.
With the company now focusing on the revised scope of funds moved and its response plan, the attribution question remains separate from the immediate need to secure withdrawals and work through the largest cross-chain theft figure Bitget says it identified.
What the bounty program signals for recovery efforts
Bitget’s Friday update included a decision to keep withdrawals paused and to launch a bounty program. While the details of how participants can qualify are not included in the article text provided, the stated purpose is clear: to encourage freezing or recovery of stolen assets.
In previous breach cases across crypto exchanges and custodial services, incentives aimed at accelerating fund discovery and coordination have become a common response pattern—particularly when assets are already moved across multiple networks. By tying the recovery push to a bounty, Bitget appears to be attempting to widen the net beyond internal controls and forensic analysis.
At the same time, the exchange’s insistence that “no further unauthorized transfers are possible” suggests it believes attackers’ ability to continue moving funds has been interrupted—though users will ultimately want confirmation as withdrawals resume and balances are reconciled.
A major industry incident, compared with other recent hacks
Even with the updated accounting, Bitget’s breach remains among the largest security incidents to hit the crypto industry. The incident is now described as causing about $388 million in affected assets, placing it in the same category of major exchange events that have shaken user confidence and forced rapid operational changes.
The article also notes a recent benchmark from earlier in the industry cycle: hackers stole about $1.5 billion worth of Ether from Bybit in February 2025. That comparison underscores how, despite improvements in security practices over time, large-scale thefts can still occur—and that recovery efforts often extend beyond the initial incident window.
For Bitget customers, the next phase will likely center on how quickly the platform can finalize asset reconciliation, whether withdrawal pauses can be lifted in stages, and how the bounty program contributes to recovering—or at least mitigating—the portion of funds that ended up in attacker-controlled addresses.
As Bitget continues its review, investors and users should watch for updates on withdrawal timelines and any additional operational details around the bounty program’s implementation, alongside evidence that the exchange’s claims of containment hold up as funds are fully traced and accounted for.