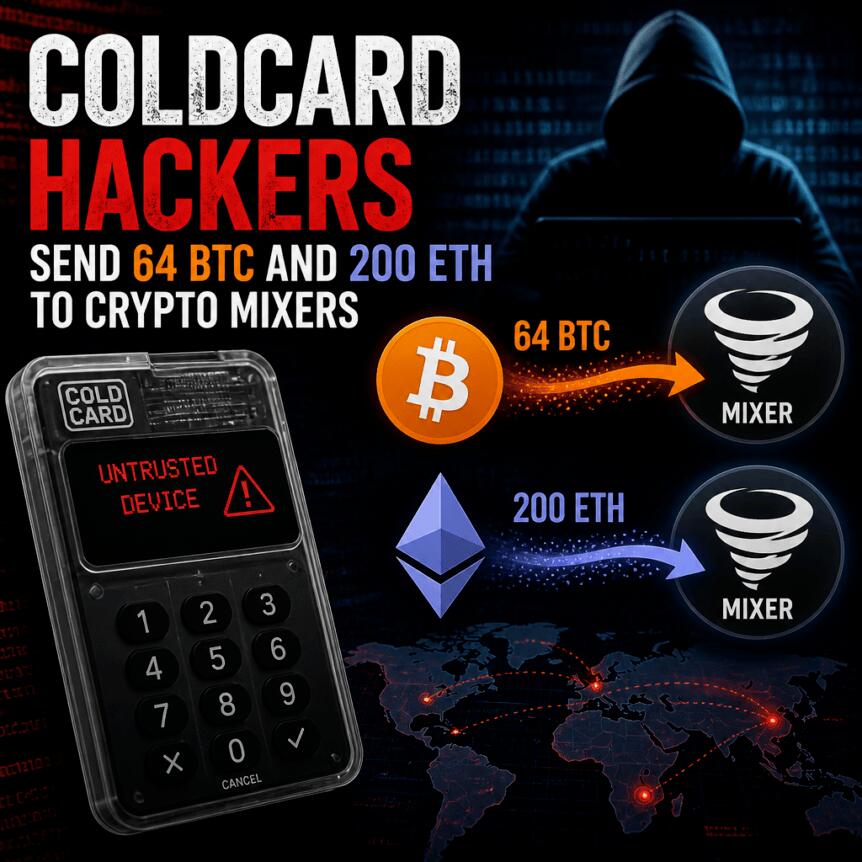
Stolen funds tied to the Coldcard hardware wallet exploit are showing early signs of laundering, but blockchain security researchers say most potential copycats have not yet moved large amounts of the victimed crypto. According to CertiK, about 64 Bitcoin (worth roughly $4.17 million) and 200 Ether (worth about $380,000) linked to the attack were routed into well-known mixing services—Wasabi for BTC and Tornado Cash for ETH.
The Coldcard incident has quickly become one of the largest crypto hacks of the year. Galaxy Digital previously put confirmed losses at least at $100 million in Bitcoin across three waves, and it also flagged a possible fourth wave that could raise total losses to around $130 million.
Key takeaways
- CertiK says roughly 64 BTC linked to the Coldcard exploit were sent to Wasabi, and 200 ETH were moved to Tornado Cash.
- Mixing services typically pool funds and obscure onchain linkages, reducing the odds of recovery for victims.
- TRM Labs’ tracing suggests most victim balances remain concentrated in a small set of attacker-controlled addresses with limited mixing activity.
- Analysis of transaction patterns across attack waves indicates the exploit may involve more than one actor.
Mixing services enter the Coldcard laundering picture
CertiK’s blockchain monitoring connected specific transfer activity to the Coldcard exploit and mapped part of the flow into privacy and obfuscation tooling. In its reporting, CertiK indicated that the Bitcoin transfer—sourced from address bc1q0—was sent to the Wasabi mixing protocol on Tuesday, using CertiK’s address data shared with Cointelegraph.
On the Ethereum side, CertiK stated that 200 ETH were sent to Tornado Cash on Wednesday, pointing to an X post from its account as the basis for the observation.
Crypto mixers like Tornado Cash operate by pooling deposits from multiple users and then releasing funds in a way that breaks straightforward onchain tracking from original sender to final recipient. That feature is precisely what makes tracing more difficult and asset recovery less likely—especially when attackers move quickly and fragment funds across multiple addresses and services.
Why this matters: laundering momentum vs. copycat behavior
CertiK’s spokesperson told Cointelegraph that the activity could be linked to a smaller exploiter, adding that “there’s likely a few copycats after the initial exploit.” The implication is straightforward: if additional parties used the same weakness, their onchain movement could help or hinder investigators depending on whether they follow up with laundering at scale.
That’s where TRM Labs’ findings become important. In a Thursday report titled “The largest hardware wallet exploit of 2026: inside the $116 million Coldcard hack”, TRM Labs said its onchain tracing indicates most victim funds were still pooled in a limited number of attacker-controlled addresses and that mixing attempts appeared restrained.
TRM Labs also highlighted that “differences in transaction construction” between each wave suggest multiple attackers. In other words, even if the underlying vulnerability was shared, the operational playbook may not be identical—an asymmetry that can be useful for investigators trying to separate participant identities, funding sources, and laundering pathways.
Coldcard hack scale and the “waves” pattern
Galaxy Digital previously characterized the Coldcard exploit as the third-largest cryptocurrency hack of 2026 so far, based on confirmed activity. In its assessment, Galaxy put drained losses at at least $100 million in Bitcoin across three verified attack waves involving 7,300 victim wallets. Galaxy also pointed to a suspected fourth wave that could lift total losses to roughly $130 million in BTC, according to earlier coverage from Cointelegraph.
Those wave-based findings matter for how analysts interpret laundering. If attackers are not distributing funds aggressively—or if only one portion of the stolen assets has been moved into mixers—then the time dimension becomes critical: investigators may still be waiting for broader follow-through as additional actors or additional batches of stolen funds begin to move.
Galaxy’s earlier analysis, also cited by Cointelegraph, suggested at least 15 different attackers exploited the vulnerability. This lines up with TRM Labs’ point about differences in transaction construction between waves, reinforcing the idea that what may look like a single incident could actually be a coordinated (or at least parallel) operation with distinct participants.
The technical weakness behind the exploit
TRM Labs’ report attributed part of the vulnerability to a firmware bug from March 2021 that weakened seed randomness on some Coldcard wallets. According to TRM Labs, the bug effectively reduced key strength to 40 bits from 128 bits, making it “brute-forceable without physical access.”
Other commentary around the fix has emphasized the low cost of better security hygiene. Dragonfly managing partner Haseeb Qureshi wrote that approximately “$2 of AI hardening” could have prevented the Coldcard exploit, referencing social media reports that some AI models rediscovered the vulnerability quickly—though those claims are framed as commentary rather than formal technical findings.
For investors and builders, the core takeaway is less about any single price tag and more about how quickly weaknesses can be weaponized once public knowledge spreads. When a vulnerability can be exploited remotely and at scale, incident response needs to account for both immediate attackers and longer-tail copycats.
Going forward, readers should watch whether additional attacker-controlled addresses begin pushing larger portions of stolen balances into mixing services, and whether the “suspected” fourth wave confirmed by Galaxy develops further. As more funds move—or fail to move—onchain, investigators will gain clearer signals about how many actors are involved and how successfully they’re managing to break traceability.