Binance disclosed it has set aside more than $6.34 billion to cover losses after hackers stole about $6.3 billion from the exchange on Thursday, an incident now described by blockchain tracing firm TRM Labs as the largest cryptocurrency theft on record. Industry partners have reportedly frozen roughly $3 billion in assets linked to the attack, but customers are still waiting for withdrawals to fully reopen.
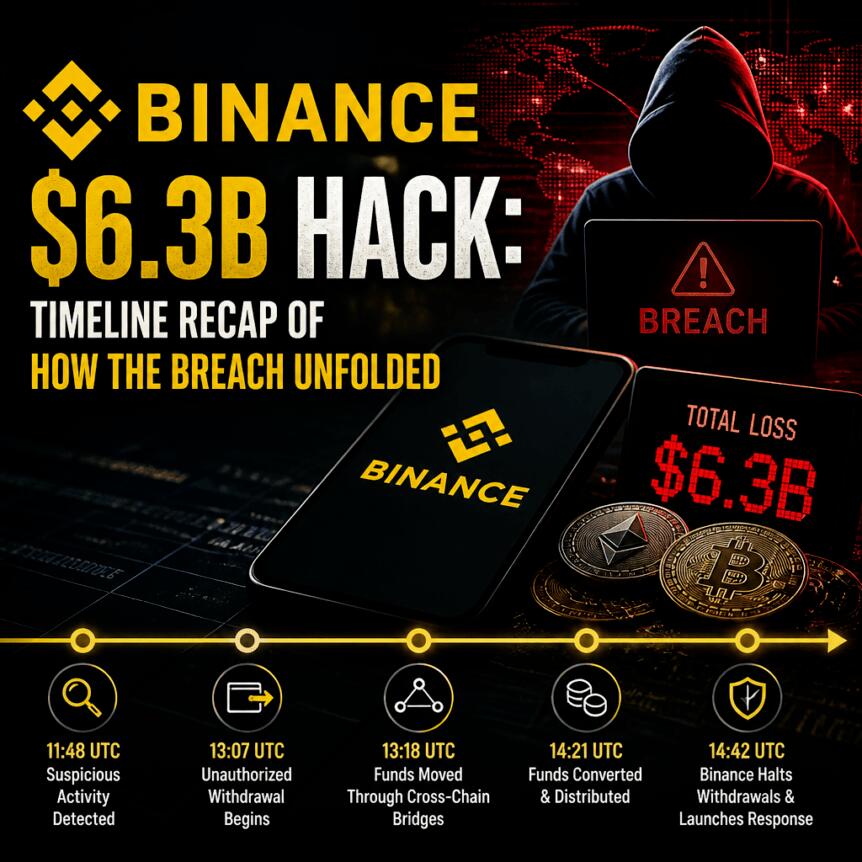
TRM Labs traced the first unauthorized transfers to around 8:05 pm UTC on Thursday, reporting that Binance wallets were drained across multiple blockchains. The attackers focused on hot wallets—accounts kept online for day-to-day withdrawal processing—according to TRM’s analysis. Binance has not publicly confirmed who was behind the hack, though TRM attributed the operation to North Korea’s TraderTraitor group, a name previously tied in the US to the $1.5 billion Bybit theft in February 2025.
Key takeaways
- TRM Labs traced initial unauthorized transfers to about 8:05 pm UTC Thursday, with drains reported across multiple blockchains.
- Partners have frozen roughly $3 billion in affected assets, but Binance has not yet detailed how much stolen crypto has been returned to its control.
- Binance says it reserved over $6.34 billion—including $5 billion already held in affected tokens—to cover losses, while buying remaining tokens via exchanges and over-the-counter deals.
- The theft has put Ethereum’s EIP-7702 feature under scrutiny, with Binance describing the attacker’s use of delegation to bypass normal approval controls.
- Binance withdrawals remain suspended as of the latest updates; Binance aims to resume withdrawals within 40 hours and publish a full proof-of-reserves report by Monday.
Tracing points to hot-wallet access and multi-chain drains
In its incident tracing, TRM Labs said it identified the first unauthorized transfers around 8:05 pm UTC Thursday and observed Binance wallets being drained across multiple blockchains. The pattern is consistent with an exchange being compromised at the operational layer—particularly if attackers gained control of keys or signing processes used by hot wallets.
TRM’s attribution to TraderTraitor was one of the most consequential claims in the early stages of reporting. The firm also tied the incident to a broader pattern of North Korean-linked activity noted by the US Federal Bureau of Investigation, which had blamed the TraderTraitor group for the Bybit theft in February 2025. Even so, Binance has not confirmed the identity of the attacker.
Binance co-CEO Richard Teng emphasized that the exchange had not reached conclusions about individual responsibility. “To be clear: the attacker did not simply use one engineer’s permissions, and this was not a single ‘one-click’ action,” Teng said, adding that Binance’s investigation “has not attributed responsibility to any individual.”
Recovery coverage vs. what is actually recovered
Binance’s financial response centers on its stated loss coverage rather than immediate recovery amounts. The exchange said it reserved more than $6.34 billion in company funds, including $5 billion already held in the affected tokens. Binance also indicated the reserved allocation excludes frozen assets, and that it plans to acquire the remaining tokens needed for coverage through exchanges and over-the-counter arrangements.
According to a spokesperson who told Cointelegraph that the $5 billion was in Binance’s custody, Binance declined to provide specific wallet addresses, citing security concerns. CertiK said it would need more information to verify the holdings independently.
This distinction matters for users assessing whether “covered” losses translate into “recovered” funds. Frozen assets are not automatically equivalent to returned assets, and Binance had not yet disclosed how much stolen crypto has actually been restored to its control at the time of the reporting. Investors and customers watching for clawback progress may therefore need to focus on future disclosures about post-freeze movement and reconciliation, not only coverage statements.
EIP-7702 controversy highlights delegation as an attack accelerant
One of the most immediate technical controversies around the Binance hack involves Ethereum’s EIP-7702. Cointelegraph reported that the upgrade came under fire after attackers used it to drain a Binance wallet.
EIP-7702 is a wallet feature that allows authorization for software to act on a wallet’s behalf. Blockaid CEO Ido Ben-Natan told Cointelegraph that compromised signing systems likely enabled the theft. He also suggested that while attackers could potentially have carried out the robbery without EIP-7702, the feature may have helped them bypass safeguards and drain assets in a more efficient “one sweep” style.
Teng’s description of the mechanism pointed to delegation behavior rather than a simple permission misuse. He said the attacker used an EIP-7702 delegation to gain execution authority over a hot wallet without going through Binance’s normal approval controls. Teng also referenced a “self-destruct mechanism” that destroyed tools and traces, complicating the investigation.
On-chain monitoring also contributed to the narrative. Chainalysis observed thousands of transactions in quick succession that it interpreted as potentially automated laundering—movements among addresses, sometimes returning to wallets used earlier—an indicator that the attackers likely planned for speed and concealment.
For Ethereum ecosystem participants, the key takeaway is not that EIP-7702 is automatically to blame, but that wallet authorization features can materially change the threat model when combined with compromised operational security. What remains uncertain is how common such delegation-based bypass attempts are, and whether exchanges and wallet providers will adapt authorization flows and monitoring controls in response.
Withdrawals suspended, while Aave restarts markets
The hack rattled activity across crypto markets and led Binance to freeze new deposits and borrowing on decentralized lender Aave as a precaution. Aave reopened its markets Friday afternoon, while Binance withdrawals remained suspended.
Binance said it was rebuilding its withdrawal service and conducting a company-wide security review. Teng stated that Binance aims to resume withdrawals within 40 hours of his Friday update and to publish a full proof-of-reserves report by Monday.
Customers and counterparties should treat these timelines as operational goals rather than guarantees. The pace of withdrawal resumption often depends on the completion of security checks, replacement of compromised components, and the stabilization of transaction processing across affected networks. Meanwhile, the proof-of-reserves report and future disclosures around frozen assets and actual re-control of funds will likely determine how quickly user trust can be restored.
As Binance works through the technical remediation and disclosure process, readers should watch for what the proof-of-reserves report covers in practice, how many frozen assets ultimately become recoverable, and whether more details emerge about the EIP-7702 delegation pattern and any systemic safeguards exchanges may tighten next.