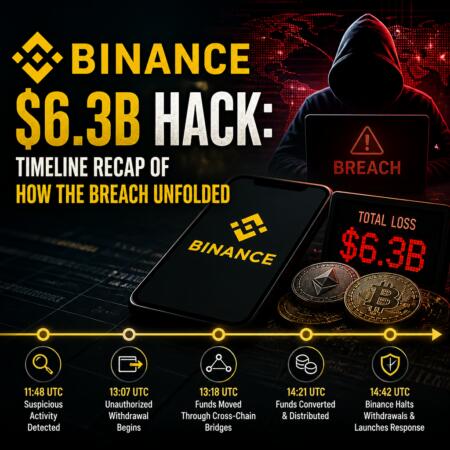
Binance’s estimated $6.3 billion hack—described by investigators as the largest in crypto history—shows how quickly major thefts can migrate from “steal” to “launder,” even as issuers and protocols move to block access. The attack began at 8:04 pm UTC on Thursday, and the suspected North Korean-linked perpetrators moved rapidly into assets they believed could be harder to freeze.
By Friday, Binance said it had frozen about $3 billion of the stolen funds onchain. Meanwhile, stablecoin issuers and other gatekeepers launched address blacklists and freeze actions that came within minutes of the initial transfers—yet the remaining portion of the attackers’ holdings still raises a central question for users and regulators: how much of the balance can actually be recovered, not just immobilized?
Key takeaways
- Binance estimates the theft totals roughly $6.3 billion, with about $3 billion frozen onchain as of Friday.
- Stablecoins led the freeze response: Tether and Circle reportedly moved within minutes of funds reaching attacker-controlled addresses.
- Attackers appear to have “pre-chosen” assets—shifting from freezeable stablecoins into Bitcoin and Ether—before restrictions fully took effect.
- Even when funds are frozen, decentralized venues like lending protocols can complicate recovery, especially when collateral has already been deposited.
- Frozen does not always mean recovered: immobilization can stop spending without automatically returning assets to the exchange or victims.
Racing the freeze: from stablecoins to BTC and ETH
According to Cointelegraph’s coverage linked in the source material, the hacking operation was tied to North Korean actors previously associated with the Bitget breach. In this incident, investigators say the perpetrators began converting captured funds immediately after the initial compromise.
The strategy was straightforward: stablecoins such as USDT and USDC are issued by centralized entities that can freeze tokens tied to specific addresses, so the attackers moved to assets that generally lack an equivalent “off switch.” In practice, that means converting into assets like Bitcoin (BTC) and Ether (ETH), where address-level freezing is far more difficult.
CertiK engineer Dickson Wu reported tracing a large slice of USDT movement—$500 million sent to a single address, with $325 million reportedly sold to market makers for ETH by 20:59 UTC, less than an hour after the hack started. This timeline aligns with Binance’s later emphasis that freezing occurred quickly, but not before meaningful conversion took place.
Stablecoin blacklists slow spending—but recovery is not guaranteed
Stablecoins are built around centralized issuance, and that structure is what made the early response possible. Unlike BTC or ETH, where no single issuer can freeze balances, tokens like Tether’s USDT and Circle’s USDC can be immobilized by their issuers at targeted addresses.
Binance stated that it was coordinating with law enforcement, issuers, and blockchain analytics firms to trace additional funds beyond the initial freeze. Tether reportedly froze roughly $1.567 billion in USDT in total, with the first major freeze action occurring about 37 minutes after the stolen funds reached an attacker-controlled Ethereum wallet. Circle reportedly froze about $823 million in USDC roughly three minutes later.
Other entities also contributed to the containment effort, and the source material notes that some decentralized systems attempted to intervene as well. For example, Arbitrum’s Security Council reportedly moved around $30.5 million in ARB and ETH into an intermediary frozen wallet, where funds could only move after additional council action or a vote by Arbitrum DAO governance.
Still, the ability to freeze funds does not automatically translate to full recovery. As the source emphasizes, immobilizing assets can prevent suspected attackers from spending them, but it does not by itself return funds to Binance or to impacted users. That distinction matters for victims, because the end goal is restoration—assets tracked, jurisdiction supported, and ultimately returned—not merely reduced attacker access.
Aave shows how “freezeability” can break down in DeFi
One of the trickiest elements in this story is what happened inside decentralized finance. The source material describes an attacker-controlled wallet depositing $60 million in USDT into Aave V3 on Ethereum between 20:58 and 21:01 UTC, then borrowing $44.6 million of wrapped Ether (WETH) about 40 minutes before the first freeze actions were reported.
LlamaRisk, an Aave risk service provider, said in its 1:00 am update that the attacker’s position later held roughly $59.9 million in USDT collateral against about $43.8 million in debt. Aave also indicated the position remained overcollateralized and did not threaten protocol suppliers.
However, this structure creates a recovery challenge. The USDT had already been deposited into Aave’s lending pool, so blacklisting the attacker’s wallet could prevent further control by the attackers, but it does not automatically retrieve collateral held by the protocol. Marc Zeller—identified in the source material as an Aave Chan Initiative founder—underscored the difference: the collateral is effectively “criminal but overcollateralized in the eyes of the protocol,” meaning the protocol remains solvent even if the counterparty is malicious.
To reduce further risk, Aave temporarily froze markets across its V3 and V4 deployments. The precautionary freeze was later lifted across those markets, with Aave stating its contracts were unaffected and that overcollateralization persisted.
How much of the stolen crypto can be kept—and what remains uncertain
Elliptic, referenced in the source, estimated that $2.84 billion had been frozen by 7:00 am UTC on Friday. The same analysis suggested the attackers still controlled about $3.33 billion in assets that issuers could not immobilize.
Even if freezes roughly halve the attackers’ available profit pool, remaining holdings may still be difficult—or slow—to recover. BTC and ETH generally lack issuer-level freezing, so once stolen funds are converted into native cryptocurrencies, blocking transactions becomes more about tracing, exchanges’ compliance actions, and law-enforcement outcomes rather than direct token freezes.
Binance has also publicly committed to covering user losses using its Secure Asset Fund for Users (SAFU) and company funds. The source material cites Binance CEO Richard Teng saying the exchange is “already recovering stolen assets for users.” In addition, Binance previously said user assets remain safe.
For market participants, the practical takeaway is that the “freeze” headline is only one part of the process. What matters next is whether remaining funds—especially those already converted into BTC and ETH—can be routed to identifiable endpoints, intercepted through exchange controls, or recovered through legal coordination.
Going forward, investors and users will want to watch whether Binance’s recovery efforts continue to expand beyond the initial frozen amount, and whether DeFi exposure—where collateral can be locked inside protocols—produces additional containment steps or requires longer-term compensation solutions.