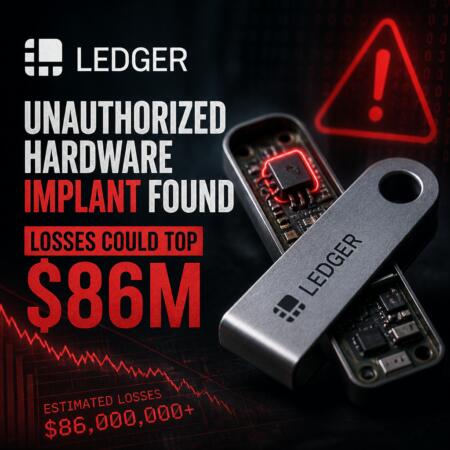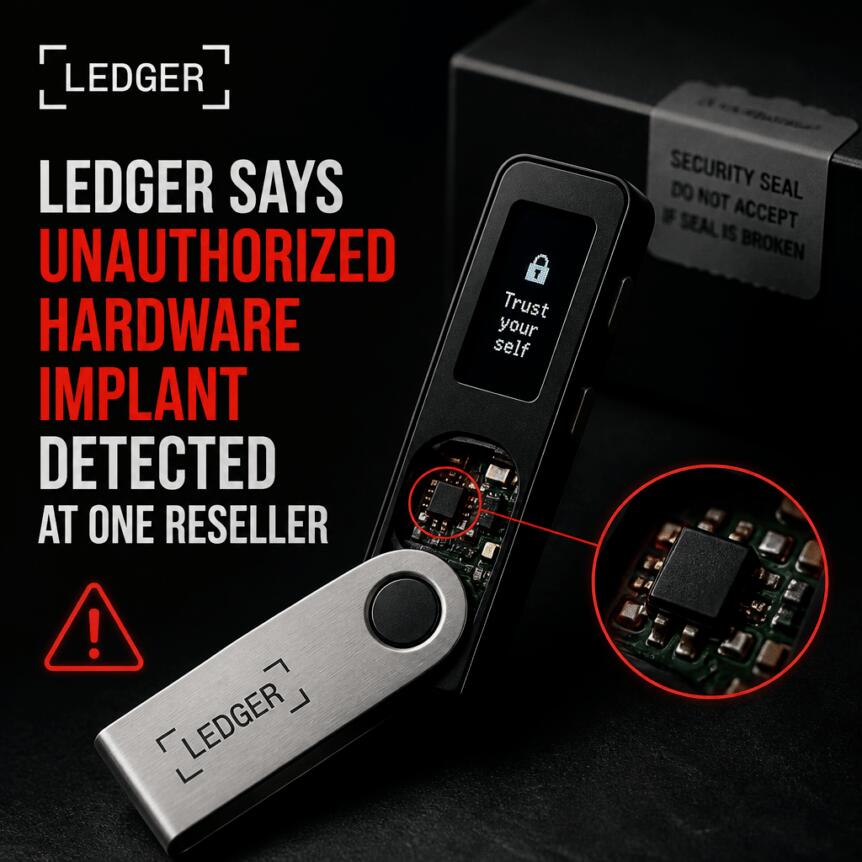
Ledger has confirmed that at least one compromised device purchased through a Southeast Asian reseller contained an unauthorized hardware implant, as the hardware wallet company continues to investigate reports of user fund losses. In an update posted to its official X account, Ledger said it is reaching out to affected customers while assessing the scope of the incident.
The company also urged users who bought Ledger devices from the identified reseller to take immediate precautions. Meanwhile, reseller CryptoBilis said it has paused sales of all Ledger hardware wallet inventory until the investigation concludes and Ledger finalizes next steps.
Key takeaways
- Ledger says one impacted device included an unauthorized hardware implant, based on its investigation findings.
- Ledger is contacting users and continues investigating; it has not disclosed the number of affected customers or total loss value.
- CryptoBilis has stopped selling Ledger devices pending the outcome of the review, and Ledger is coordinating with the reseller.
- Ledger recommends not initiating setup for new devices from the reseller and, if already set up, moving funds to a new Ledger device (new seed).
Ledger confirms unauthorized hardware on an impacted device
In a Sunday post on X, Ledger said it is responding to the reports tied to devices purchased from the Southeast Asian reseller CryptoBilis. Ledger’s statement indicates that the incident involved a tangible compromise of hardware—an unauthorized implant discovered on one of the reported devices—rather than a claim about wider penetration of Ledger’s internal infrastructure.
Ledger also said it was continuing to contact users as part of the ongoing investigation. Specter, an investigator monitoring the case, estimated that losses could total more than $86 million across Bitcoin, Ethereum, and Tron. Ledger has not verified how closely those estimates reflect the final figure, but the company did emphasize that it remains in active review.
What users should do if they bought from the reseller
Ledger’s guidance focuses on preventing further exposure and reducing the risk that a compromised device could be used to move or authorize funds.
For customers who purchased a Ledger device from the reseller but have not completed setup yet, Ledger recommended they do not initiate the setup process. The rationale is straightforward: if hardware has been tampered with, running initialization steps may expose the wallet’s security assumptions.
For customers who already set up their devices, Ledger advised users to move assets to a new Ledger signer created with a new seed phrase. That effectively severs any potential linkage between the compromised hardware and the user’s security posture going forward.
Reseller pauses sales as Ledger coordinates next steps
CryptoBilis, the reseller at the center of the investigation, confirmed in Ledger’s update that it had stopped selling all Ledger hardware wallet inventory until the probe is complete. Ledger said it is actively communicating with CryptoBilis about next steps, indicating the remediation process may involve both operational controls and further verification around affected supply batches.
Earlier reporting from Cointelegraph noted that CryptoBilis was listed as an authorized Ledger reseller in Indonesia, Malaysia, and the Philippines. While that context matters for how customers may have purchased devices through legitimate channels, Ledger’s latest update frames the issue as isolated to the single reseller and its market.
Ledger says its systems were not compromised
Ledger stated that the incident appears limited to the reseller relationship and does not reflect a compromise of Ledger’s broader security environment. In its statement to Cointelegraph, Ledger said: “Ledger’s infrastructure, systems and services were not compromised,” adding that its investigation is still ongoing.
That distinction is important for users trying to evaluate risk. If Ledger’s systems and services were not breached, the primary threat model shifts toward supply-chain tampering and device-level compromise—meaning customers who obtained devices through specific channels may face a different risk profile than those who purchased elsewhere.
Ledger also said it had not confirmed how many customers may be affected or the value of the losses described in the reports. In the meantime, the company invited individuals with information relevant to the investigation to contact its bounty program at bounty@ledger.fr.
Where the investigation goes next
As Ledger continues its inquiry, the most important questions for wallet owners remain unanswered: how many devices are implicated, which specific batches and timelines are affected, and what verification steps users can rely on before resuming normal use. Until Ledger provides further detail, customers should follow the company’s setup and fund-migration guidance for any device purchased from the flagged reseller channel.