Blockstream CEO Adam Back may have long played down the immediacy of quantum threats, but the company he leads is moving forward with concrete work on how Bitcoin could upgrade if sufficiently powerful quantum computers ever become a practical reality. That progress just received a fresh milestone: a Bitcoin Improvement Proposal (BIP) for the company’s experimental post-quantum signature scheme, SHRINCS, was published on the project’s GitHub repository.
The development matters because Bitcoin’s current elliptic-curve signature system (used for spending authorization) is widely understood to be vulnerable to the key-recovery capabilities of future quantum machines. While the exact timeline remains debated, cryptographers agree the worst-case scenario would allow attackers to derive private keys from public keys and steal funds—making migration planning an industry priority rather than a reactive scramble.
Key takeaways
- Blockstream published a BIP for SHRINCS, positioning it as an actionable candidate for Bitcoin’s post-quantum signature upgrade path.
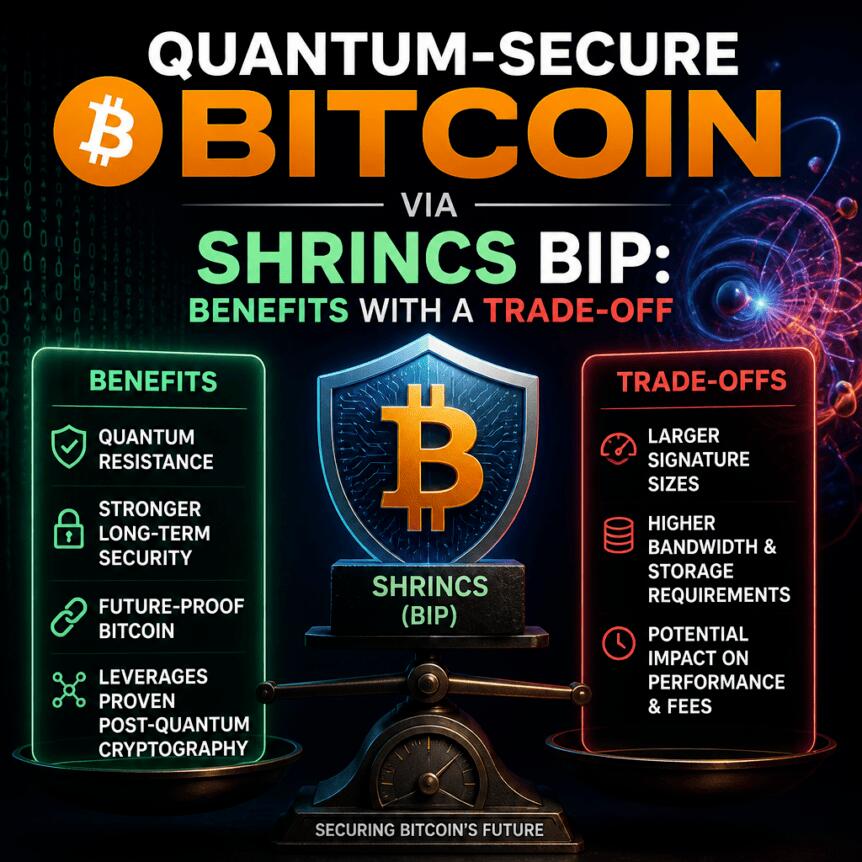
- SHRINCS is designed to be “Bitcoin-native” and smaller than many NIST-aligned post-quantum signature alternatives, helping it fit Bitcoin’s block and witness constraints.
- The proposal’s approach is more “stateful,” which can reduce on-chain size but introduces wallet/device recovery and interoperability risks.
- Blockstream’s ongoing research explores complementary ideas—like signature-size reduction and potential ZK proof aggregation—while keeping governance and deployment decisions separate.
From quantum skepticism to BIP-level implementation
Adam Back has been associated with a cautious stance toward quantum timelines—arguing in earlier comments that the threat may not materialize for decades. Yet, Blockstream’s work shows how even a “farther away” threat can justify engineering now: building, testing, and documenting cryptographic changes before the political and technical window closes.
Blockstream Research has previously demonstrated SHRINCS as an experimental post-quantum signature scheme operating in production on Liquid, a Bitcoin sidechain. The new BIP—published earlier today in the SHRINCS repository—takes that experimental work and frames it explicitly for Bitcoin improvement discussions.
Jonas Nick, a Blockstream Research researcher, characterized the BIP as “the first concrete proposal” for a post-quantum signature scheme built specifically around Bitcoin’s needs. He also cautioned that SHRINCS is not presented as Bitcoin’s “final” signature design and is not optimal on every dimension—an important distinction for investors and builders trying to evaluate how close a proposal is to consensus-level readiness.
Why signature size is the core Bitcoin constraint
In most post-quantum signature designs, public parameters and signature payloads are substantially larger than Bitcoin’s current elliptic-curve signatures. According to the article’s cited comparison, NIST-endorsed post-quantum hash- and lattice-based signature schemes are between 38 and 123 times larger than Bitcoin’s ECDSA and Schnorr signatures. The practical consequence is straightforward: larger signatures mean more data per transaction, which can reduce throughput.
The same reporting notes that deploying those larger NIST-style signatures directly in Bitcoin could push performance down to a fraction of a transaction per second. Ethereum’s post-quantum team, as referenced in the article, has discussed addressing the blockspace problem by aggregating signatures using a small zero-knowledge proof per block—an approach that, if feasible, can reduce on-chain footprint. Bitcoin, however, would face a different social and technical hurdle: adding ZK proof aggregation would represent a major change to the system’s validation and activation politics.
Blockstream’s alternative is to shrink the signature payload itself. The approach discussed here aims to reduce Bitcoin-relevant signature sizes by about 13.23 times compared with baseline NIST-aligned hash-based post-quantum signatures, while retaining enough compatibility with Bitcoin’s operational constraints to keep the upgrade conversation realistic.
What SHRINCS targets—and what trade-offs it makes
The SHRINCS design was unveiled by Blockstream researchers in December 2025, with an opcode proposal published in May. It is a hash-based post-quantum signature scheme built to work within Bitcoin’s signature-size realities. The scheme is reported as having a minimum size of 548 bytes plus a 48-byte public key, with maximum sizes that can reach 4,619 bytes.
A key selling point is “Bitcoin-native” construction: one cited explainer describes the scheme as real code signing real transactions on Liquid mainnet and as an attempt to address post-quantum migration without breaking Bitcoin’s block economics. That said, it remains early-stage research. The article references a warning embedded in the BIP text that a formal security proof is “TODO,” indicating the cryptography is promising but not yet fully validated at the level Bitcoin-style upgrades normally demand.
Even with SHRINCS’s improvements, the scheme is still described as significantly larger than current Bitcoin signatures—about nine times larger than Schnorr signatures (64 bytes). The report also emphasizes that the impact is not as simple as a “9x blocksize increase,” because Bitcoin’s Segregated Witness changes how signature bytes are accounted for in block weight.
Where SHRINCS makes a more controversial engineering choice is in its state management. Traditional stateless designs can store everything required to verify and update signatures in the public structure, but they often require large signature artifacts. The article describes SHRINCS as intentionally reducing those artifacts by using one-time keys and keeping track of “used keys” on the device—meaning the scheme behaves in a stateful way.
This can affect users in concrete ways. Each time a signature is used, it adds roughly 16 bytes to the signature. More importantly, if a device is lost, the fallback mechanism can require a very large transaction (the article cites about 5,777 bytes) to recover. Additionally, the BIP warning cited in the article notes that different SHRINCS implementations may not interoperate safely if they use incompatible stateless-component settings—raising the risk of lost funds during key import.
That tension—smaller signatures in exchange for operational fragility—is likely to shape governance debates more than raw cryptographic novelty. Bitcoin’s consensus rules are permanent maintenance obligations, and wallet-side assumptions can become user failure modes.
Iterating for deployment: hardware wallets, SHRIMPS, and options for aggregation
Blockstream says it has continued refining SHRINCS through 2026 and recently demonstrated that SHRINCS and other post-quantum signature schemes can run on common hardware wallets. That is not a trivial detail: even well-designed cryptography can stall adoption if it cannot fit the performance and memory constraints of real wallet environments.
The article also references work on a companion backup/derivation concept. Earlier in March, Blockstream introduced “SHRIMPS” to support signing by backup devices initialized from the same seed in a way that aligns with SHRINCS signing behavior. In the BIP update described here, the SHRIMPS naming is dropped and the scheme is incorporated as a built-in stateless path under the same 48-byte public key, optimized with a non-standard parameter set to be about 26% smaller.
Beyond hash-based signatures, Blockstream’s research also experiments with lattice-based signature approaches, which are often smaller but described as less proven and less reliable than hash-based designs in the current literature. The article further notes Blockstream’s consideration of zero-knowledge proof aggregation. According to its estimates, pairing ZK aggregation with SHRINCS could potentially double Bitcoin’s speed in this modeled scenario.
Notably, Blockstream is reported to have separated signature-choice work from the separate, more contentious questions of block size increases and ZK aggregation. That decision reflects a pragmatic recognition: pairing multiple disruptive changes at once can make it harder to build consensus. If Bitcoin is to migrate to post-quantum security, the pathway likely needs modular governance milestones rather than one all-at-once overhaul.
As one explained perspective cited here puts it, the “binding constraint” may not be cryptography alone but governance—how Bitcoin chooses among a growing menu of engineering options (including references to other proposals like BIP-360, BIP-361, and STARKs) before an upgrade clock runs out.
For readers, the next signal to watch is whether the SHRINCS BIP gains traction in the broader Bitcoin development and review ecosystem—particularly around its stateful design risks, key recovery/fallback behavior, and interoperability guarantees between wallet implementations. The proposal’s publication is a meaningful step from experimentation toward deployment planning, but the hard part will be convincing the network that the trade-offs are acceptable and the security path is complete enough for consensus.