North Korea-linked hackers have reportedly turned to memecoins as a laundering tool, according to blockchain analytics firm Elliptic. In a new report, Elliptic says the group created fresh tokens on the NEAR blockchain and routed small portions of stolen Binance funds through decentralized exchange liquidity pools—transactions that, despite appearing on-chain, drew almost no outside participation before being abandoned.
The findings add to a growing pattern of how sophisticated laundering can hide inside the mechanics of decentralized finance. For investors and exchange operators, the episode is a reminder that “low volume” tokens can still be used as vehicles to move illicit proceeds, even when public attention is minimal.
Key takeaways
- Elliptic attributes the scheme to North Korean-linked actors using memecoins as laundering vehicles after the $6.3 billion Binance hack.
- Between Nov. 5 and 7, Elliptic says at least six tokens were created on NEAR and used via DEX liquidity pools to move $430,000 in stolen funds.
- The tokens reportedly attracted almost no outside trading and were discontinued shortly after launch.
- Elliptic says a similar method was previously used after the 2025 Bybit hack, involving a newly created token on TRON through which at least $24 million was moved.
- Meanwhile, regulators in Asia are moving toward more proactive controls around crypto platform operations during suspected cyber events.
Memecoins as a laundering layer after the Binance hack
Elliptic’s report centers on laundering activity tied to the major Binance hack, which the firm links to North Korea-linked hackers. Rather than relying on conventional transfers alone, the actors reportedly manufactured new tokens and then used decentralized exchange infrastructure to shuffle funds across wallets.
According to Elliptic, between Nov. 5 and 7 the hackers created at least six tokens on NEAR. They then used liquidity pools on decentralized exchanges to transfer $430,000 of stolen cryptocurrency between wallets. The goal, as Elliptic frames it, was to complicate attribution by introducing additional on-chain steps that can resemble ordinary trading activity—at least superficially.
Crucially, Elliptic reports that the tokens did not meaningfully engage the broader market. The memecoins attracted almost no external trading before being abandoned shortly after launch. That detail matters: it suggests the tokens were not intended to build liquidity for legitimate trading, but rather to serve as short-lived conduits for moving funds.
Elliptic also published a write-up of the technique, noting that it reflects a broader evolution in laundering tactics that blend illicit capital movement with token issuance and DEX mechanics. The report can be found here: Elliptic. Earlier coverage is available via Cointelegraph.
The same playbook appeared after the Bybit hack
Elliptic says the laundering approach is not unique to the Binance incident. The firm reports that the same general method—creating a token and then moving funds through decentralized exchange-related activity—was also used after the $1.5 billion Bybit hack in 2025.
In that earlier case, Elliptic reports that North Korean-linked actors moved at least $24 million using a newly created token on the TRON blockchain. As with the NEAR memecoin approach, the underlying idea is to insert additional token-related activity into the path of illicit funds, making investigation and tracing more time-consuming.
From an investigative standpoint, the continuity of technique is significant. When the same group uses the same “vehicle,” analysts can sometimes identify recurring signatures—such as how tokens are created, funded, and then abandoned—alongside wallet patterns and DEX interactions. For compliance teams at exchanges and custodians, these repeated patterns can inform risk scoring and monitoring even when token names change or projects look fresh.
Why short-lived tokens still matter to exchanges and users
At face value, memecoins with almost no public trading can look like noise. Elliptic’s report argues that this apparent lack of market relevance can be misleading.
When illicit actors create tokens quickly and route stolen value through liquidity pools, the transaction flow may mimic parts of legitimate DeFi activity. Even if outsiders don’t trade the asset much, the on-chain mechanics can still be used to redistribute funds across addresses, potentially reducing the clarity of simple “source-to-destination” trails.
For exchanges, this has practical implications. Monitoring systems that focus only on heavily traded assets could miss laundering activity carried out through low-visibility tokens. Custodians and compliance teams may need to expand heuristics beyond volume—incorporating token creation patterns, liquidity pool interactions, and timing relationships between token launches and fund movements.
It’s also a reminder for traders and DeFi users: a token’s low external activity does not necessarily imply benign origins. In high-risk periods—especially after major breaches—token issuance and DEX routing patterns can be used to test new laundering routes.
Asia policy and operational moves: proactive suspension powers and licensing
While Elliptic’s report focuses on laundering tactics, other developments across Asia show regulators emphasizing operational controls and oversight. In South Korea, the Financial Services Commission (FSC) plans to allow exchanges to suspend deposits and withdrawals when hacking is suspected, rather than waiting for a breach to be conclusively confirmed. The FSC said it would issue a no-action letter permitting preventive suspensions under defined conditions, noting that current rules generally prohibit blocking withdrawals without legitimate grounds and only explicitly allow restrictions when hacking is clearly established. The regulator also called for round-the-clock monitoring, stronger cold-wallet holdings, and improved insurance and reserves.
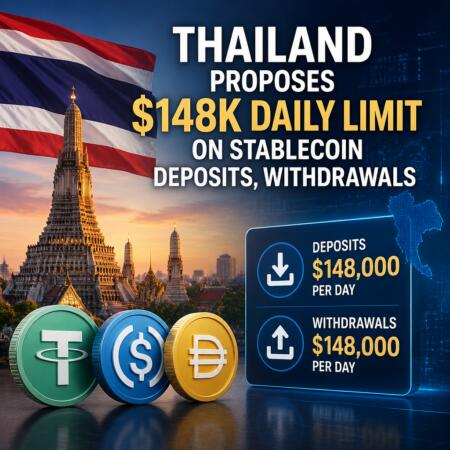
In Thailand, the securities regulator proposed measures intended to reduce abuse of stablecoin flows. The draft caps daily stablecoin deposits and withdrawals at 5 million baht (about $148,000) per customer at regulated crypto operators, and it would apply separately to deposits and withdrawals at each operator. The proposal is also described as part of efforts to curb money laundering, cybercrime, and attempts to bypass cross-border transfer rules; it would bar stablecoin transfers to and from third-party wallets.
Hong Kong, meanwhile, is preparing a broader licensing framework for virtual-asset services. Deputy Secretary for Financial Services Chan Ho-lim said the region would introduce a licensing regime for virtual-asset trading, custody, advisory, and management through amendment bills submitted to the Legislative Council this year.
Separately, operational risk management is also visible in market behavior. GOPAX, a South Korean exchange, announced that it suspended trading, deposits, and withdrawals and moved user assets to cold wallets after receiving threatening emails alleging an imminent hack, acting on recommendations from financial authorities.
Across these jurisdictions, the common thread is a shift toward faster, better-defined responses to suspected risks—whether those risks involve cyber incidents or suspicious asset flows.
As regulators tighten oversight and analytics firms document new laundering methods, the next thing to watch is whether exchanges and custodians expand monitoring to include low-liquidity token creation and DEX pool interactions—not just high-volume trading. Elliptic’s findings also raise a wider question for the industry: how consistently these token “vehicles” are being reused after major breaches, and what measurable signals could help detect them earlier.